“The PHP security team would like to give advance notice of an upcoming security release. It is scheduled for Wednesday, 21 October 2026 at 14:00 UTC. It addresses two critical vulnerabilities, both rated CVSS v4.0 9.2.”
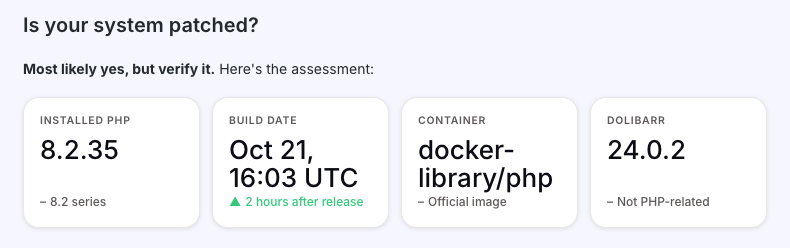
The php.net archive shows security releases in the 8.2 series up to at least 8.2.33/8.2.34, and the critical release was scheduled for today at 14:00 UTC. Your image was built at 16:03 UTC the same day – i.e. two hours after the release time – and version 8.2.35 sits above the earlier security releases mentioned. This strongly suggests your container is already running the patched version (e.g. if the image was pulled/restarted this afternoon).
But to verify: Since the PHP team had not yet published which exact version number contains the critical fix, you should double-check on the php.net ChangeLog for 8.2 that 8.2.35 is the current security release – or simply pull the latest image once more (podman pull + restart) to guarantee you’re up to date.
And when I look at the changelog for 8.2, it seems like version 8.2.35 has the necessary fixes.
That phpinfo page (Home > Admin tools > PHP info) is the right place to check, since it shows what the web server really runs. Safe versions are 8.2.35, 8.3.36, 8.4.27 and 8.5.12 or newer; anything older in those branches is not fixed. After updating, restart Apache or PHP-FPM and check the page again. One catch: Debian/Ubuntu packages can carry the fix under an older version number, so check the package changelog if in doubt. Docker users: the 8.2.35 tags did land, as Florian said.
I updated my Dolibarr (from 19-24.02) and all worked fine. (although it seemed that some recent invoices weren’t showing on the main dashboard, they were still present).
Then I updated my PHP from 8.1 to 8.4, and how I am unable to log-in to Dolibarr.
I get the error on the top saying , “**Security token has expired, so action has been canceled. Please try again.”
**
I have erased the only module I had installed in /custom (TOTP 2FA), but I’m still getting the error.